abap_jwt_generator
Generates a signed JSON Web Token in ABAP from an explicit header and claim, a stored profile in table ZJWT_PROFILE, or a shared secret, signing through a PSE profile or with the secret.
zcl_jwt_generator builds a JWT from a header and claim it is given, signing it through a PSE profile with generate_jwt, or derives one directly from a named entry in table ZJWT_PROFILE with get_jwt_by_profile; get_access_token_by_profile returns an access token the same way. generate_jwt_with_secret signs a token with a shared secret instead of a certificate, matching what a tool like a JWT debugger would produce. It stops at producing the token: what it is presented to, and how that side validates it, is outside the repository.
Facts
Where it sits
Who is behind it

In the atlas: maintains 1, contributes to 2@abapChaoLiumaintainerJaime Rodriguez CapoteContributes to this

In the atlas: maintains 1, contributes to 9@jrodriguez-rcLars HvamContributes to this

In the atlas: maintains 13, contributes to 92, wrote 1@larshp2 contributors
Before choosing this
Signals
ActivityQuietNo published releases; repository quiet for 68 months
It publishes no releases, and its repository has been quiet for at least 24 full months. This may be normal for stable software; check whether its current state still fits your use.
What it declares
Every artifact
- Type
- Package
- Origin
- Independently maintained
As a package
- Where it runs
- does not say
- Distributed through
- does not say
Connections
Establishing who is calling and making that identity available
Download
README
quoted from abapChaoLiu/abap_jwt_generator under MIT, read
ABAP JWT Generator
Generate Json Web Token (JWT) in ABAP.
Demo 1 - method get_jwt_by_profile().
If JWT profile is maintained in table ZJWT_PROFILE, use method get_jwt_by_profile() to derive JWT token by profile name.
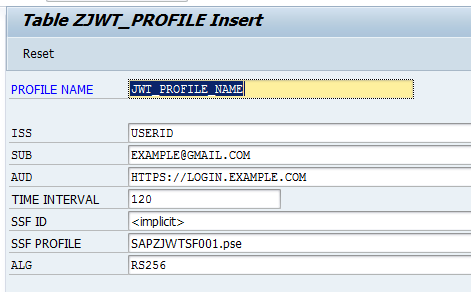
DATA: jwt_generator TYPE REF TO zcl_jwt_generator,
      jwt TYPE string.

CREATE OBJECT jwt_client.
jwt = jwt_client->get_jwt_by_profile( 'JWT_PROFILE_NAME' ).
Demo 2 - method generate_jwt().
If JWT profile is not maintained, use method generate_jwt() to derive JWT token.
REPORT zrpt_jwt_generator_demo.

DATA: jwt_generator TYPE REF TO zcl_jwt_generator.
DATA: jwt_header TYPE zcl_jwt_generator=>ty_jwt_header,
      jwt_claim  TYPE zcl_jwt_generator=>ty_jwt_claim.
DATA: exp_second        TYPE int8,
      ssf_info           TYPE ssfinfo.
DATA: start_timestamp TYPE timestamp VALUE '19700101000000',
      ssf_id          TYPE ssfid VALUE '<implicit>',
      "PSE profile with private key
      ssf_profile     TYPE ssfprof VALUE 'SAPZJWTSF001.pse'.


jwt_header-alg  = 'RS256'.
jwt_claim = VALUE #(  iss = 'UserID'
                      sub = 'example@gmail.com'
                      aud = 'https://login.example.com'
                      exp = exp_second ).

ssf_info = VALUE #( id = ssf_id profile = ssf_profile ).

CREATE OBJECT jwt_generator.
TRY.
    jwt_generator->generate_jwt(
      EXPORTING
        jwt_header     = jwt_header
        jwt_claim      = jwt_claim
        ssf_info       = ssfinfo
      RECEIVING
        jwt            = DATA(jwt) ).
  CATCH zcx_jwt_generator INTO DATA(lo_exp).
    WRITE /: 'ERROR when generate JWT token.'.
    WRITE /: lo_exp->get_text( ).
ENDTRY.
Demo 3 - method get_access_token_by_profile().
If JWT profile is maintained in table ZJWT_PROFILE, use method get_access_token_by_profile() to get JWT Access Token.
DATA: jwt_generator TYPE REF TO zcl_jwt_generator,
      jwt_access_token TYPE string.

CREATE OBJECT jwt_client.
jwt_access_token = jwt_client->get_access_token_by_profile( 'JWT_PROFILE_NAME' ).
Demo 4 - method generate_jwt_with_secret().
You can use method generate_jwt_with_secret() to generate a JWT with the secret key, like JWT Debugger.
GET TIME STAMP FIELD DATA(timestamp).

DATA(jwt_generator) = NEW zcl_jwt_generator( ).

TRY.
    DATA(jwt_result) =
        jwt_generator->generate_jwt_with_secret(
            jwt_header = VALUE #( alg  = 'HS256' typ = 'JWT' )
            jwt_claim  = VALUE #( sub  = '1234567890'
                                  name = 'John Doe'
                                  iat  = jwt_generator->convert_abap_timestamp_to_unix( timestamp ) )
            secret     = '1WRAv0Usf90-jr2W7UQBQBLvIBBFq8vumq-VzrR3h7E'
            algorithm  = 'SHA256' ).
  CATCH zcx_jwt_generator INTO DATA(lx_jwt).
ENDTRY.
Credits and references
Class ZCL_JWT_Generator is modified from Dimitri Seifmann's post Connect from AS ABAP to Google Cloud Platform App-Engine resource secured with Google Identity-Aware Proxy.
Others providing
Compare all 23 on the Authentication page →- @arc-mcp/xsuaa-auth@arc-mcp/xsuaa-authThe client-to-server authentication stack for an MCP server on SAP BTP: an XSUAA OAuth proxy, dynamic client registration, a chained bearer verifier, and a separate entrypoint for per-user principal propagation.independent, btpXSUAA authentication stack for an MCP server on SAP BTPfrom BTP/BAIP
- abap-pwnedpasswordsabap-pwnedpasswordsChecks from ABAP whether a password appears in the Have I Been Pwned breached-password list, wrapping the Pwned Passwords API V3 in one call that answers with a boolean.independent, abapChecks passwords against Have I Been Pwned from ABAPfrom ABAP
- SAP Authorization and Trust Management serviceSAP Authorization and Trust Management serviceThe OAuth server behind a BTP application: issues the JWT the app checks, holds the scopes and role collections it checks against, and brokers trust to an identity provider. Bound, never installed.sap official, btpOAuth server issuing JWTs and holding scopes for BTP appsfrom BTP/BAIP
- Cloud Identity ServicesCloud Identity ServicesIdentity Authentication and Identity Provisioning as one tenant: the login, the user store or the federation to a corporate identity provider, and the provisioning of users into whatever sits behind it.sap official, btpIdentity Authentication and Identity Provisioning as one tenantfrom BTP/BAIP
- SAP Customer Identity and Access Management for B2CSAP Customer Identity and Access Management for B2CSAP's customer identity service: registration, login and consent for the users of a company's websites and apps, kept in one profile per customer, with regional data storage and risk-based authentication as options.sap official, btpRegistration, login and consent for customer-facing sitesfrom BTP/BAIP
- OAuth 2.0 on SAP BTPOAuth 2.0 on SAP BTPOAuth 2.0 protection for applications and APIs on SAP BTP, listed in Neo regions: the authorization code grant for web applications and the client credentials grant for API and IoT scenarios.sap official, btpOAuth 2.0 grant flows for applications and APIs in Neo regionsfrom BTP/BAIP
- com.sap.cds:cds-feature-identitycom.sap.cds:cds-feature-identityThe CAP Java feature that validates OAuth2 tokens from XSUAA and SAP Cloud Identity Services and builds the request's security context from them.sap official, capOAuth2 token validation from XSUAA and SAP Cloud Identity Servicesfrom CAP
- com.sap.cds:cds-feature-xsuaacom.sap.cds:cds-feature-xsuaaThe CAP Java feature that validated XSUAA-issued JWTs, published up to 2.10.7 before CAP Java 3.0 removed it in favour of com.sap.cds:cds-feature-identity.sap official, capFormer XSUAA JWT validation for CAP Java, removed in CAP Java 3.0from CAP
- abapOAuthAzureabapOAuthAzureAn Enhancement Spot OA2C_SPECIFICS implementation for Microsoft Azure, written against ABAP's OAuth 2.0 Client API, with a one-sentence README that leaves configuration to SAP's help page.independent, abapOA2C_SPECIFICS implementation for Microsoft Azure OAuth 2.0 in ABAPfrom ABAP
- abap2oauth2abap2oauth2An ABAP API for OAuth 2.0 authentication that registers a provider's client ID and secret as a named consumer and implements signature method 3, the one Google uses.independent, abapABAP API for OAuth 2.0 authenticationfrom ABAP
- abapNTLMabapNTLMAn HTTP NTLM client for ABAP, with the RC4, MD4 and DES algorithms the protocol needs implemented in ABAP, which its maintainer says seems to work only some of the time.independent, abapHTTP NTLM client for ABAPfrom ABAP
- abap_cloud_platformabap_cloud_platformA TypeScript library of the Cloud Foundry calls that walk down to an ABAP service instance, read its SAP_ADT service key and log a user in, so a tool outside the system can reach it.independent, btpTypeScript library reaching ABAP service instances on Cloud Foundryfrom BTP/BAIP
- decodesapsso2decodesapsso2A TypeScript library that decodes a MYSAPSSO2 logon ticket into its user, client, system and validity fields, and returns the signature without validating it, so it never shows a ticket is genuine.independent, abapTypeScript decoder for MYSAPSSO2 logon ticketsfrom ABAP
- @marianfoo/sap-mcp-auth@marianfoo/sap-mcp-authA shared browser-login and session module for SAP MCP servers: it drives a Playwright browser through SAP Identity Authentication, caches the session cookies and returns a cookie header an HTTP client can send.independent, btpBrowser login and session module for SAP MCP serversfrom BTP/BAIP
- @sap/approuter@sap/approuterSAP's Node.js application router: the single entry point in front of a business application's microservices, which authenticates the user, forwards each request to a backend by route and serves static content.sap official, btpSAP's Node.js application router in front of business applicationsfrom BTP/BAIP
- @sap/cds@sap/cdsThe CAP Node.js runtime, which compiles the CDS model, serves the services declared in it, answers generic requests before any handler runs, and loads every cds-plugin.sap official, capCAP Node.js runtimefrom CAP
- Cloud ConnectorCloud ConnectorSAP's on-premises agent that links SAP BTP applications to systems in a customer's own network, as a reverse invoke proxy that exposes only the systems and resources it is configured to allow.sap official, btpSAP's on-premises agent linking SAP BTP to customer-network systemsfrom BTP/BAIP
- @sap/xssec@sap/xssecToken validation and security context for XSUAA and IAS.sap official, capToken validation and security context for XSUAA and IASfrom CAP
- cds-azure-adcds-azure-adAzure AD and Azure AD B2C as a custom-defined authentication strategy for CAP through passport-azure-ad, implementing the hook capire documents so the application does not validate tokens itself.independent, capAzure AD and Azure AD B2C authentication strategy for CAPfrom CAP
- @saptools/cf-xsuaa@saptools/cf-xsuaaA command line and Node.js API that reads the XSUAA binding of a Cloud Foundry app and prints an OAuth2 client_credentials token for it, cached until it expires.independent, btpOAuth2 token fetcher for a Cloud Foundry app's XSUAA bindingfrom BTP/BAIP
- cds-common-jwt-supportcds-common-jwt-supportJWT authentication for CAP without xsuaa or xssec, validating tokens with jose instead, for a service that authenticates against an identity provider other than XSUAA; last released in April 2022.independent, capJWT authentication for CAP without xsuaa or xssecfrom CAP
- abap-aws-sigv4abap-aws-sigv4Signs outbound HTTP calls to AWS APIs with AWS Signature Version 4, directly from ABAP.independent, abapSigns outbound HTTP calls to AWS APIs with AWS Signature Version 4, directly from ABAP.from ABAP
Details
Sources
Sources are graph entities: the same page may back several entries, and an unreachable source flags every row that rests on it.
Compatibility and provenance
abaplint
Contributors
History in the atlas
- First seen.
For your agent
- Ref
artifact:abapchaoliu-abap-jwt-generator- JSON
- /artifacts/abapchaoliu-abap-jwt-generator.json
- MCP
- Connecting an agent