SAP-samples/btp-secure-development
A hands-on OWASP Top 10 workshop that exploits and then fixes security flaws in a CAP Node.js application, covering broken access control, SQL injection and audit logging for sensitive data.
Each exercise follows the same structure: overview, vulnerable code, exploitation, remediation, then verification, applied to one vulnerability from the OWASP Top 10 list in a CAP Node.js application. The exercises published so far cover broken access control (horizontal and vertical privilege escalation), SQL injection, and audit logging for sensitive-data access in local development, fixed using SAP BTP's built-in security services.
Facts
Where it sits
Who is behind it

In the atlas: maintains 222@SAP-samplesmaintainerAbdelkaderDeContributes to this
In the atlas: contributes to 2@AbdelkaderDechcohrsContributes to this

In the atlas: contributes to 5@chcohrsjadolfContributes to this

In the atlas: contributes to 5@jadolfAbdelkader AbdelazizContributes to this

In the atlas: contributes to 2@Kaderde4 contributors
What it declares
Every artifact
- Type
- Sample
- Origin
- By SAP
As a sample
- Form
- Workshop or CodeJam material
Connections
Recording who touched personal or sensitive data, for auditors
Deciding who may read or change what, down to instance level
Download
Architecture
as 2 deployment descriptors state it at 487002d, readDownload
Bound, and not drawn
- incident-management-srvSAP Destination service, hana, SAP Authorization and Trust Management service, SAP Audit Log service
- incident-management-db-deployerhana
- incident-management-ui-deployerSAP HTML5 Application Repository service for SAP BTP
- incident-management-destinationsSAP Authorization and Trust Management service, SAP HTML5 Application Repository service for SAP BTP, SAP Destination service
- incident-management-app-deployerSAP Authorization and Trust Management service, SAP HTML5 Application Repository service for SAP BTP
Bound in the descriptor, not joined to an entry
hana
Download
Bound, and not drawn
- incident-management-srvSAP Destination service, hana
- incident-management-db-deployerhana
- incident-management-ui-deployerSAP HTML5 Application Repository service for SAP BTP
- incident-management-destinationsSAP Authorization and Trust Management service, SAP HTML5 Application Repository service for SAP BTP, SAP Destination service
- incident-management-app-deployerSAP Authorization and Trust Management service, SAP HTML5 Application Repository service for SAP BTP
Documented, with no instance in the document
- @cap-js/hana requires SAP HANA Cloudincident-management-srvconditionalThe database this is the service for: capire's standard database for production, reached with the credentials
cds watchorcds runfetch from the binding at runtime.Using SAP HANA Cloud for Production — capire, Prepare for ProductionThis configures deployment for SAP HANA. The configuration is added to a `[hybrid]` profile in your _package.json_.
Using SAP HANA Cloud for Production — capire, cds deployWith this information, `cds watch`/`run` can fetch the SAP HANA credentials at runtime, so that the server can connect to it.
Databases — capire, overview (the 2 is the page's footnote mark)in production, SAP HANA 2 is used by default
- @sap/xssec requires Cloud Identity Servicesincident-management-srv
Bound in the descriptor, not joined to an entry
hana
README
quoted from SAP-samples/btp-secure-development under Apache-2.0, readDeveloping Secure Solutions With SAP BTP: Proven Techniques For The Real World
📝Description
This repository contains the material for the workshop called "Developing Secure Solutions With SAP BTP: Proven Techniques For The Real World". Try it out.
🔎 Overview
Welcome to this hands-on workshop dedicated to embedding security into your SAP BTP applications. In an era where data breaches and cyber threats are constant, building secure software is not an option - it's a requirement. This workshop is designed for developers working with the SAP Cloud Application Programming Model (CAP) and Node.js.
By completing the exercises, you will gain the practical skills to identify and mitigate common security risks as defined by the OWASP Top 10 Vulnerabilities.
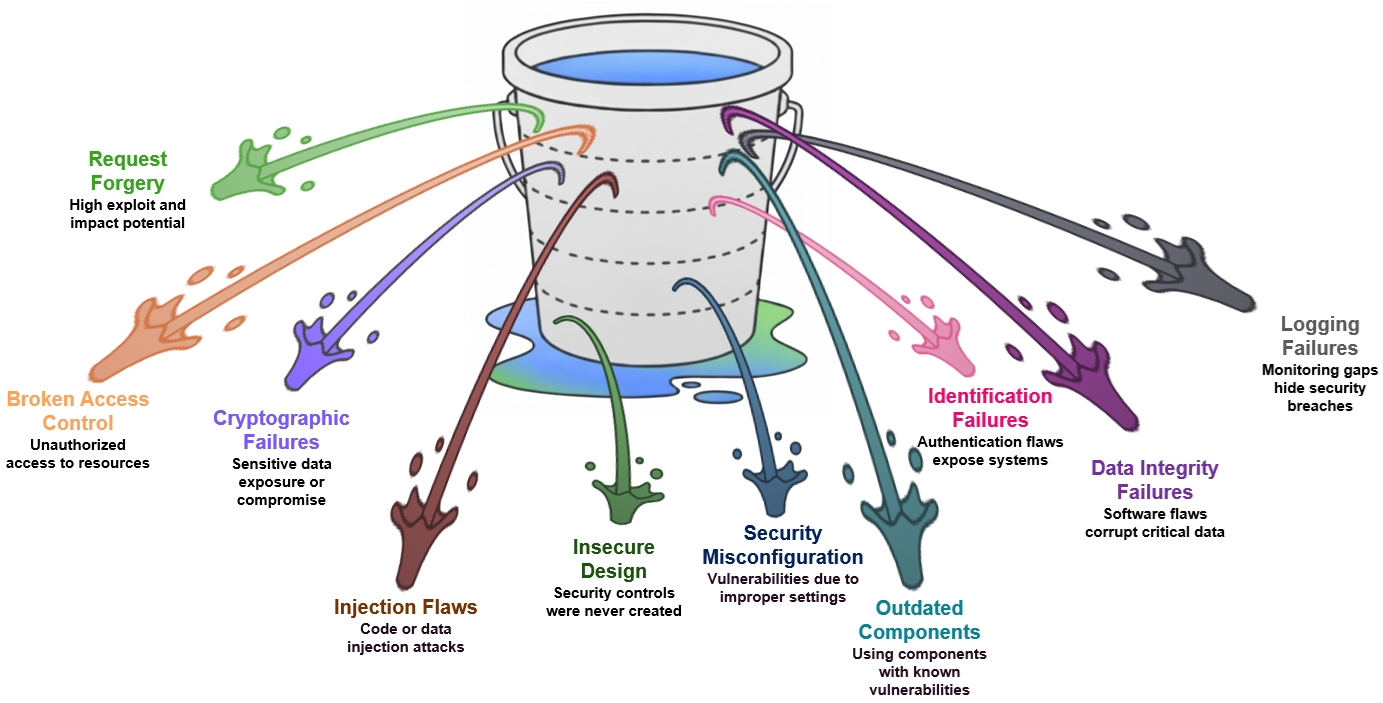
Top 10 OWASP Vulnerabilities
🎯 Learning Objectives
- Identify and Mitigate a critical OWASP Top 10 vulnerability in a real-world scenario.
- Leverage the SAP Cloud Application Programming Model (CAP) for secure, cloud-native development.
- Implement SAP BTP's comprehensive, built-in security services to protect your data and business logic.
- Validate the effectiveness of security fixes through practical testing.
📋 Requirements
- Some experience with Node.js and GitHub will be helpful.
🔧 Prerequisites
Please complete the following setup before the workshop:
- Getting Started – Set up your environment and initial deployment.
💡 Tip:
- Some exercises require switching between user accounts. Use an Incognito (Private) browser window to avoid authentication conflicts.
- This workshop was tested with the Edge web browser. For a better experience, we recommend using Edge.
💻Exercises
Every exercise module is a self-contained lab focused on a specific vulnerability. All modules adhere to the following standard structure:
-
📖 1. Overview: A high-level description of the vulnerability, its impact, and why it's a security risk.
-
🚨 2. Vulnerable Code: A snippet of code containing the specific security flaw. We'll analyze why it's insecure.
-
💥 3. Exploitation: A step-by-step guide on how to exploit the vulnerability, demonstrating its real-world impact.
-
🛡️ 4. Remediation: The corrected version of the code that patches the vulnerability, along with an explanation of the fix.
-
✅ 5. Verification: A simple procedure to confirm that the patch has successfully mitigated the vulnerability and the exploit no longer works.
-
📌 6. Summary: A practical recap that consolidates the exercise outcomes with actionable takeaways.
-
💡In step 4, you will replace the vulnerable version of the code with a corrected version. In most cases you will have to open the corrected file and copy the full content into the development environment. If you only copy the code snippet explaining the fixes, your application won't work. To copy the content of the file, use the button "Copy raw file" in the toolbar above the file content.
This structure is designed to help you understand a vulnerability from an attacker's perspective and a defender's, see how it can impact a CAP application, and learn actionable steps to mitigate it with SAP BTP best practices.
- Exercise 0 - Getting Started (Prerequisites)
- Exercise 1 - Broken Access Control
- Exercise 2 - SQL Injection
- Exercise 3 - Security Logging and Monitoring Failures
- Additional Resources
Known Issues
No known issues.
🤝 How to Get Support
Live support will be available from facilitators during the event.
🕐 Outside the Workshop
-
Found a bug or have a question?
Open an issue in this repository. -
Looking for broader support?
Ask a question in SAP Community.💡 Tip: When creating issues, please include details like your environment (Node.js version, OS), steps to reproduce the issue, and screenshots if applicable. This helps us provide faster, more accurate support!
Contributing
If you wish to contribute code, offer fixes or improvements, please send a pull request. Due to legal reasons, contributors will be asked to accept a DCO when they create the first pull request to this project. This happens in an automated fashion during the submission process. SAP uses the standard DCO text of the Linux Foundation.
License
Copyright (c) 2026 SAP SE or an SAP affiliate company. All rights reserved. This project is licensed under the Apache Software License, version 2.0 except as noted otherwise in the LICENSE file.
History
Notes
This release is intended to provide a hands-on experience for participants to explore and expand upon during the workshop. It serves as a starting point for building a secure incident management solution, with room for customization and enhancement as the workshop progresses. Use this starter kit as your base and get ready to dive into the world of secure incident management!
Details
Sources
Sources are graph entities: the same page may back several entries, and an unreachable source flags every row that rests on it.
Compatibility and provenance
Flavors
“This workshop is designed for developers working with the SAP Cloud Application Programming Model (CAP) and Node.js.” — SAP-samples/btp-secure-development — README
Contributors
History in the atlas
- First seen.
For your agent
- Ref
artifact:sap-samples-btp-secure-development- JSON
- /artifacts/sap-samples-btp-secure-development.json
- MCP
- Connecting an agent